

Security and what the agent can reach
The page a reviewer will want before approving this server.
The page a reviewer will want before approving this server.
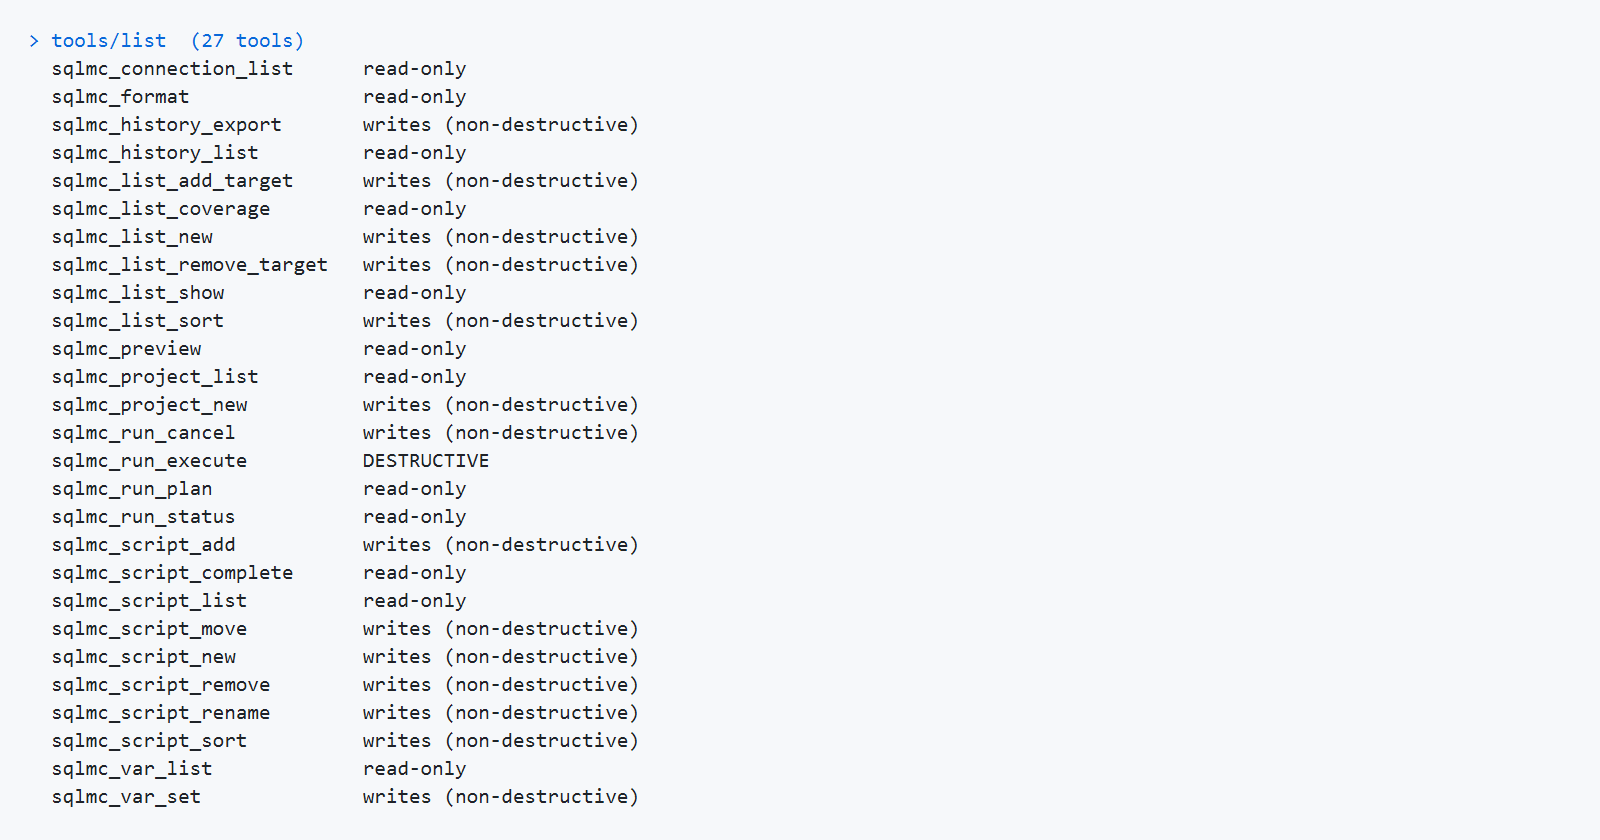
- Both tools are read-only. Neither writes to a database or to a file. The annotations say so and the implementation has no write path.
- Credentials are the launching user's. The server reads the same DPAPI-backed store as the desktop app, scoped by the OS to the account it runs as. Run it as yourself and it sees your saved passwords; run it as a service account and it sees none.
- Production is still something to agree to.
sqlmc_list_coveragenames production members in its plan and will not read them on an unconfirmed call. Reading a catalog is harmless; connecting to production on an agent's initiative is not. - Pin the workspace. The workspace an agent reaches is whatever resolution finds (§3). Set
SQLMC_WORKSPACEor passworkspaceexplicitly rather than depending on a working directory that may not be what you think it is. - What is not protected, plainly: an agent that can call these tools can read your schema and enumerate your registered servers — names, hosts, databases, and which are flagged production. It cannot read table data, cannot execute SQL, and cannot see a password. If enumerating your estate is itself sensitive, that is the decision to make before wiring this up, not after.